 CYBERDETECT
1
Connect & configure
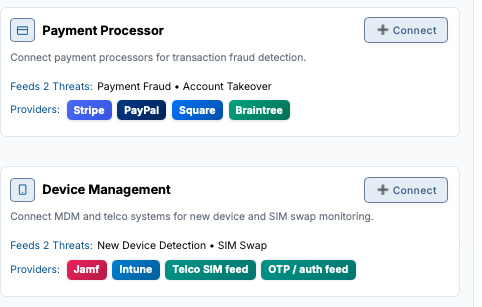
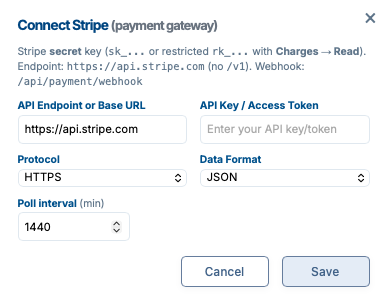
Choose integrations and add credentials — each card shows which detection packs it feeds.
The detection gap
When identity, mobile, and email attacks slip through as normal activity, the damage shows up as drained accounts, bypassed MFA, and stolen funds — not breach headlines.
Sources: Javelin Identity Fraud Study 2026; FBI IC3 Annual Report 2025 (US reported losses)
Detection packs on one platform — connect your sources, detect across domains, and alert Slack, Teams, or SOAR from day one.
Separate alerts from your tools, linked into one incident
Account takeover chain · Critical
Ready for Slack / SOAR
Concept preview — built for this page
Connect your sources, detect across them, and respond in Slack, Teams, or your SOAR the same day.
Choose integrations and add credentials — each card shows which detection packs it feeds.
Events from identity, payments, email, telco SMS, MDM, network, and application logs pass through the ML engine — scoring, correlation, and your enabled packs on every sync.
The incident reaches Slack, Teams, your SOAR, or email. Your team reviews it in Threat Explorer and acts in the systems they already run.
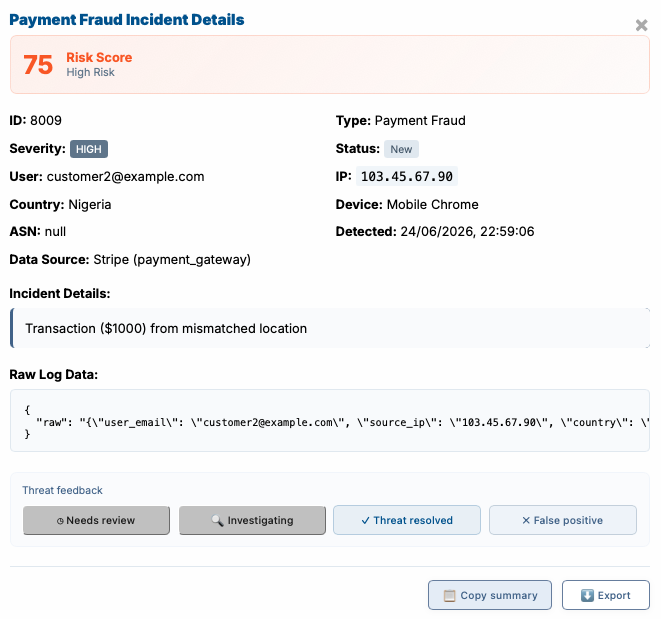
CYBERDETECT stays out of the payment path and the carrier core. Your team takes the action.
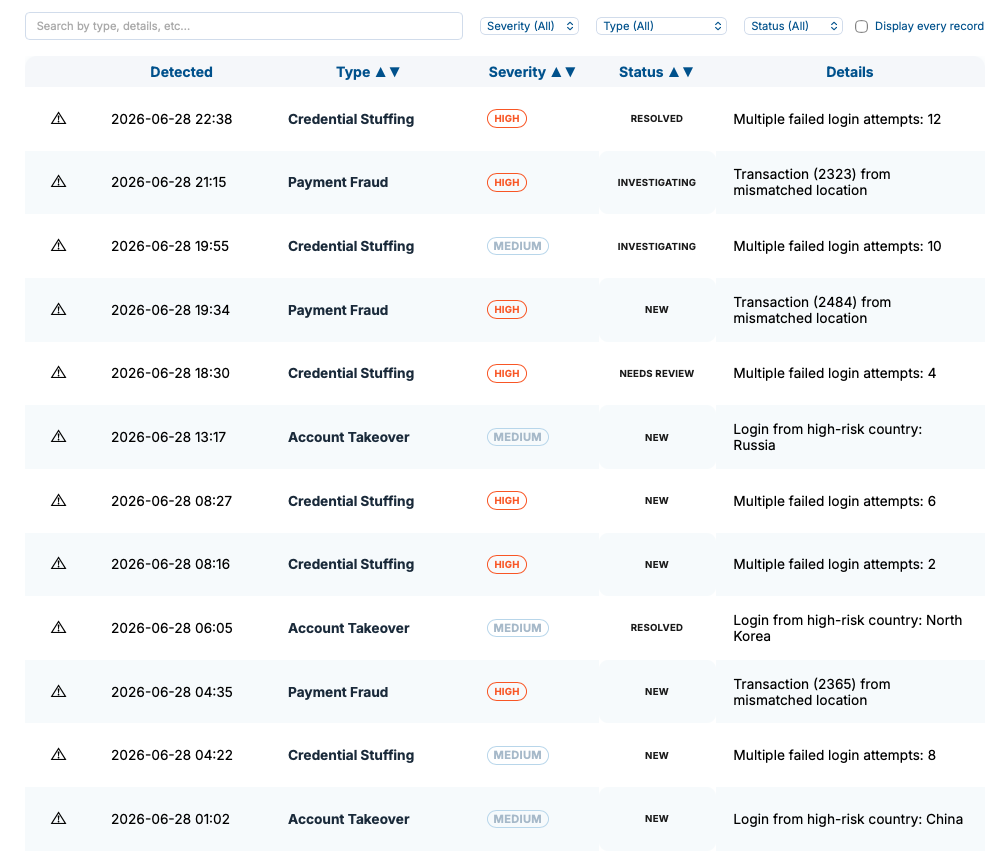
Live feed, KPIs, severity trends, and operations — the same workspace after you connect.
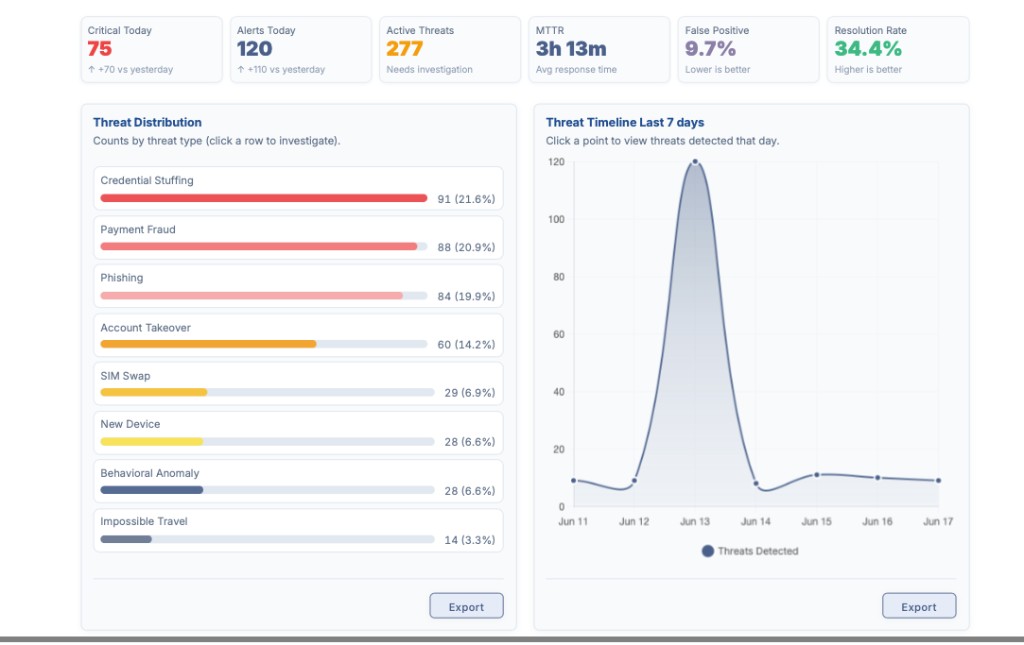
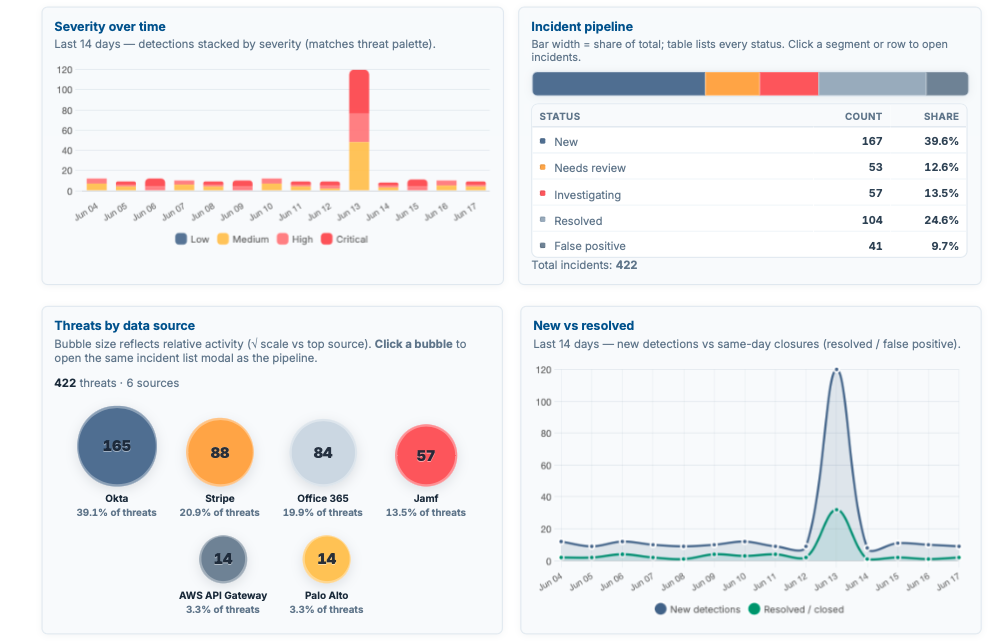
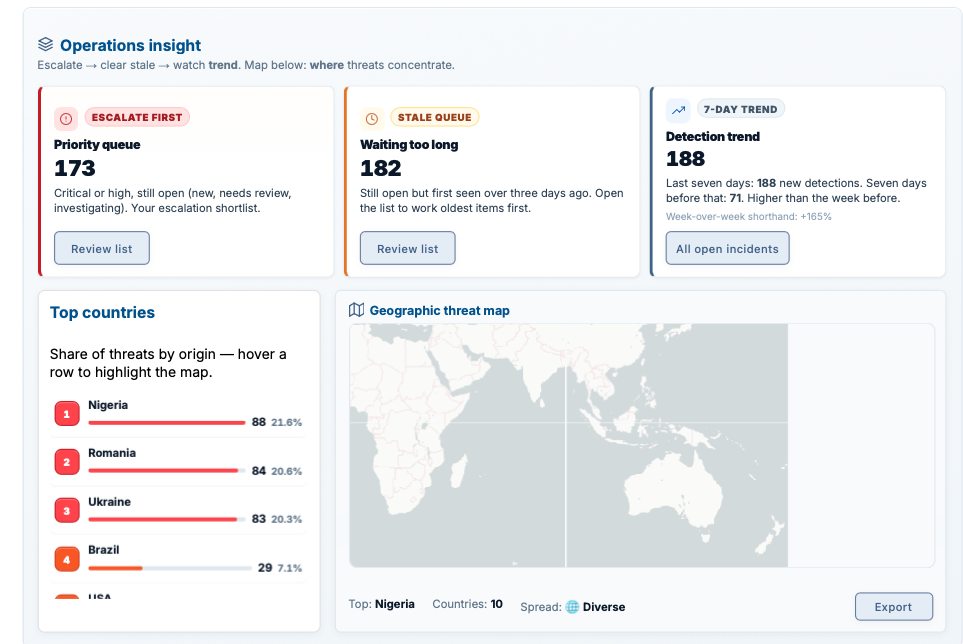
Turn on the packs that match your feeds — modules stay separate for alerts; packs keep the catalog clear.
Account takeover and abuse of logins, devices, and one-time codes.
Fraud across processors, wallets, and ATM / card channels.
Subscriber identity abuse on the mobile network.
Email + SMS social engineering — malicious links and brand impersonation.
Catch-all for novel and cross-domain patterns other packs miss.
Connect your systems, detect fraud that hurts revenue and trust, and get live alerts to Slack, Teams, or SOAR from day one.
Speed to value
Detect on day one.
No long SIEM rollout.
Faster response
Alert Slack, Teams, or SOAR.
Real-time threat triage.
Consolidate spend
One subscription only.
One vendor, one renewal.
One workspace
Alerts, triage, and export.
No patchwork of tools.
Protect revenue
Stop fraud before chargebacks.
Cut abuse-driven churn.
Limit the damage
Contain identity hits fast.
Before losses spread out.
Cross-domain view, API-first connect, and optional hybrid — without a heavy rollout.
Identity, payments, and behavior correlated in one place.
Rules plus ML — including behavioral anomaly.
High-impact threat types built in and ready to enable.
Connect data sources securely — no installation required.
Optional on-prem agent when data must stay local.
API integrations with your providers, plus controls for data handling, access, and infrastructure.
TLS for transport and encryption at rest for alerts, indicators, and configuration.
Deployed on AWS with mature security controls, logging, and hardening practices.
On-prem agent for Enterprise when sensitive data must stay local.
Start with a full-platform trial, then choose a production tier with our team — licensing is quoted after scoping.
All detection packs, full dashboard, and threat sensitivity tuning — one user.
| Capability | Trial | Starter | Enterprise | Pro | Pro+ | Tailored |
|---|---|---|---|---|---|---|
| Detection packs | All | Scoped | Scoped | All | All | Custom |
| Users | 1 | 2 | 3 | 5 | 5 | Custom |
| Custom integrations | — | — | 2 | 4 | 4 | Custom |
| Threat sensitivity | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Full dashboard | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Custom pack | — | — | — | ✓ | ✓ | ✓ |
| Hosting | Cloud-based | Cloud-based | Cloud-based | Cloud-based | On premise | By agreement |
Production tiers (Starter through Pro+ and Tailored) are priced on request after we understand your volume, integrations, and deployment model.
Contact salesTell us what you’re trying to detect and we’ll suggest the best plan and setup.
Thanks. We'll reply at that email.